Snyk Review 2026 - AI Security Platform
Verified Oct 20, 2026 by Tooliverse Editorial
Snyk scans the code your AI writes, the agents that write it, and the apps you build with it. Start free in minutes, no credit card, and fix vulnerabilities with 85%-accurate AI autofixes.
How to EASILY Check for Vulnerabilities with Snyk
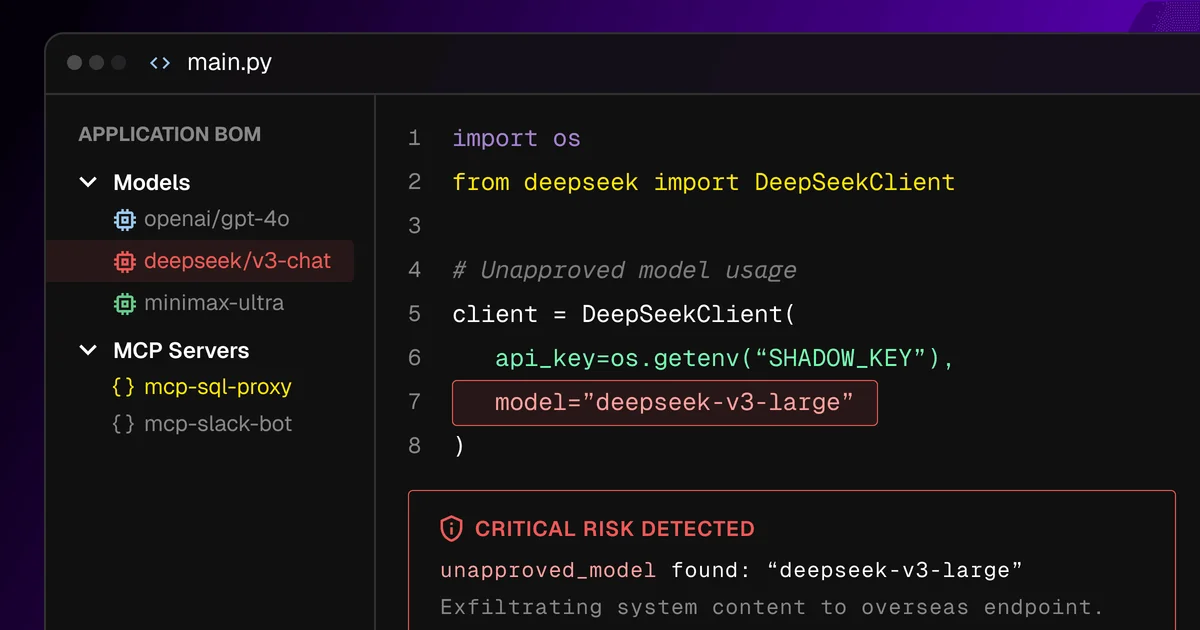
Detect critical risks from unapproved AI model usage and data exfiltration.
Unleash AI innovators securely with Snyk's new AI Security Fabric.
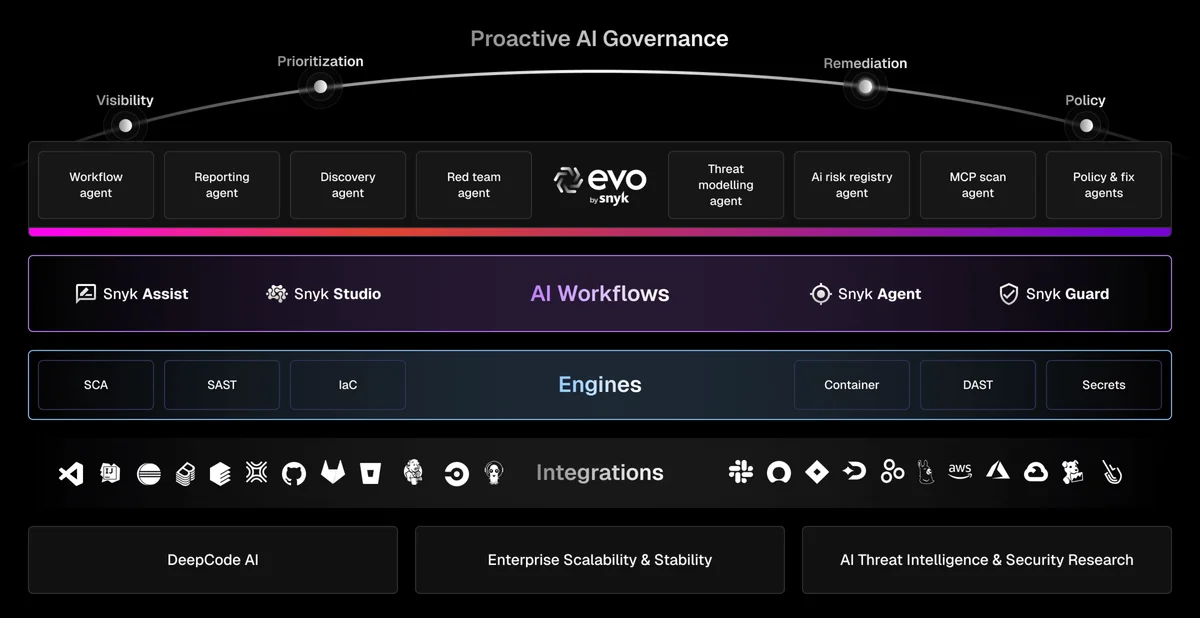
Visualize Snyk's comprehensive platform for Proactive AI Governance.
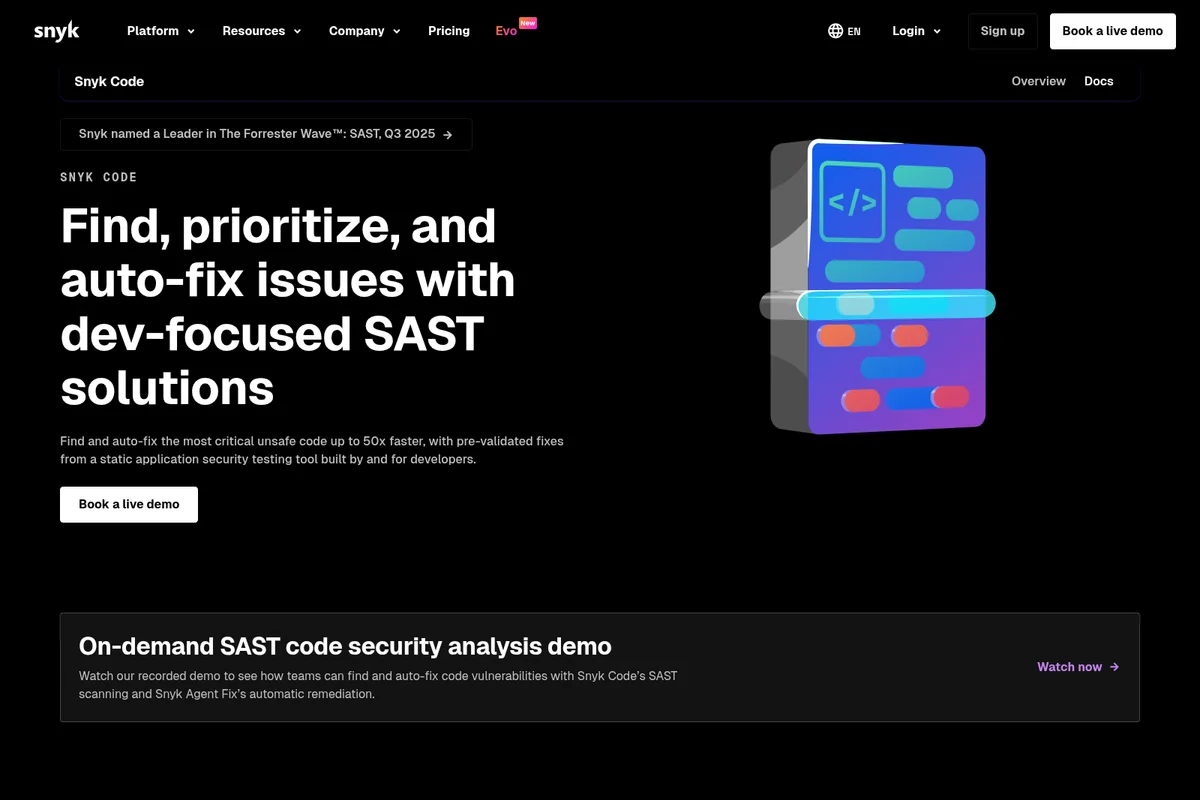
Find, prioritize, and auto-fix code security issues efficiently.
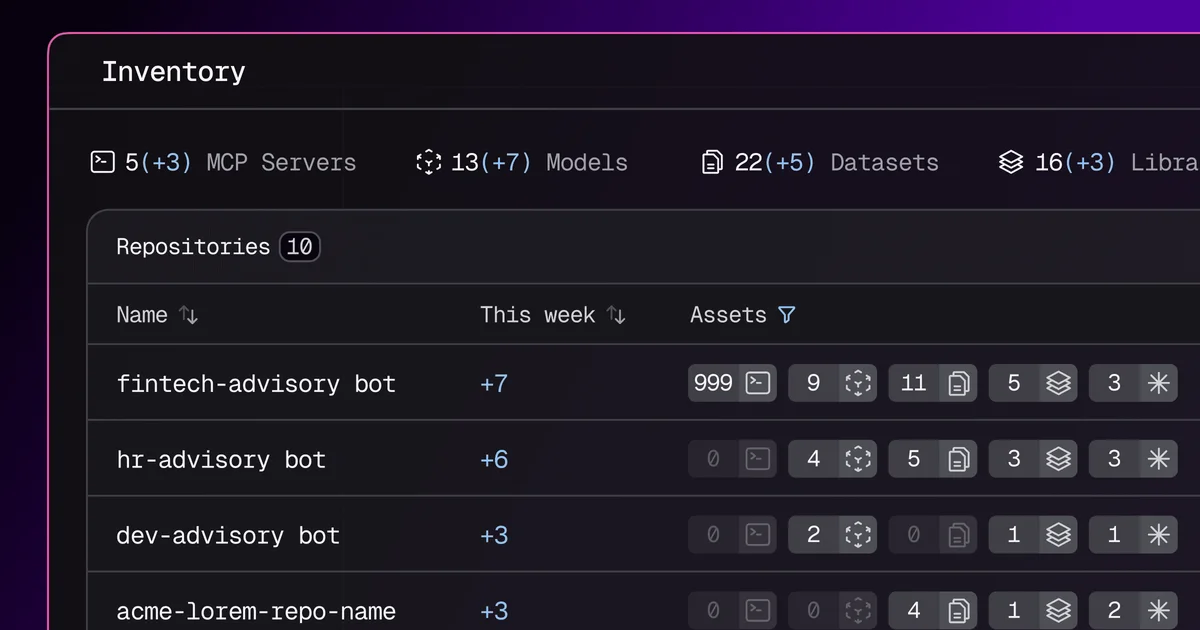
Track repositories, assets (models, datasets) and their weekly activity.
Snyk Review: Tooliverse Consensus




Based on 1k+ verified reviews across 6 platforms,
combined with Tooliverse's expert analysis
Snyk puts security findings where developers already work, pairing IDE and CI/CD scanning with fix suggestions and automated pull requests that shrink the gap between detection and repair. Reviewers single out its deep vulnerability database and container and infrastructure-as-code coverage as reasons it earns a spot in production pipelines. The catches are real: enterprise pricing strains smaller budgets, false positives demand manual triage, and large repositories can slow the IDE. Teams that budget for tuning get a scanner developers actually act on.
Bottom line: A top-tier developer-first security scanner whose actionable fixes and CI/CD integration win over engineers, though steep enterprise pricing and occasional false positives mean smaller teams should start with the cheaper plans.
Snyk | Key Specs
- Platforms
- Web, API, CLI, IDE plugins
- Pricing Model
- Freemium ($0-25/mo) + Enterprise credits See plans
- Privacy/Data Use
- AI trained on open source, never customer data; GDPR compliant
- Security
- SOC 2 Type II, ISO 27001, ISO 27017 See details
Wins
- •Integrates directly into developer workflows to catch vulnerabilities before they reach productionmentioned in 412 reviews
- •Provides actionable remediation advice that helps developers fix security issues quicklymentioned in 385 reviews
- •Scans containers and infrastructure-as-code files to ensure full-stack security coveragementioned in 294 reviews
Watch-Outs
- •Enterprise pricing tiers can be prohibitively expensive for smaller organizationsmentioned in 156 reviews
- •Generates occasional false positives that require manual triage and investigationmentioned in 112 reviews
- •Scanning large repositories can lead to significant performance slowdowns in the IDEmentioned in 89 reviews
Snyk Features 2026
Snyk Code (SAST)
Secures code as it's written with real-time static analysis powered by DeepCode AI.
Snyk Open Source (SCA)
Detects vulnerable dependencies and supports risk-based prioritization with reachability analysis.
Snyk Container
Keeps base images and container workloads secure, with registry and Kubernetes scanning.
Snyk IaC
Finds and fixes infrastructure-as-code misconfigurations in-code.
Snyk User Reviews
Selected Reviews
"Snyk has completely changed how we handle security. Instead of waiting for a security team to flag issues, my IDE tells me exactly what's wrong and how to fix it immediately."
"Snyk's integration with GitHub Actions is flawless. It's now a mandatory part of our deployment pipeline to ensure no high-severity bugs slip through."
"Great tool, but the pricing for the enterprise tier is getting out of hand. We love the features, but it's hard to justify the cost for a mid-sized team."
More from the Community
"The automated PR fixes are a lifesaver. It doesn't just find the bug; it opens a pull request with the updated dependency. Saves us hours every week."
"The VS Code extension is snappy and doesn't bloat my environment. It catches things I would have missed in my package.json files every single time."
"Scanning is thorough, but I wish the reporting was more customizable. Exporting data for our compliance audits is still a bit of a manual headache."
"I use the mobile app to keep an eye on project health while I'm away from my desk. It's simple but effective for quick status checks."
"The container scanning is top-notch. It found vulnerabilities in our base images that other scanners missed. Very impressed with the database depth."
"Actionable advice is the key. Most scanners just give you a list of problems; Snyk gives you the solution. That's the difference for a busy dev."
"The UI is clean and intuitive. Even our junior developers were able to start fixing security issues on day one without much training."
"It's a bit heavy on resources when scanning large monorepos. My laptop fans definitely kick in, but the results are worth the wait."
"Reliable and fast. The vulnerability database is clearly the best in the business right now. It's our go-to for all open source security."
Snyk Pricing 2026
View SourceFree covers more than a trial: four core scanners across five projects, enough to judge whether the IDE workflow sticks. Team at $25/month is the realistic pick for a group of up to ten developers, since 1,000 Code tests per month and Jira integration remove the first ceilings you'll hit. AI pentesting and coding agent security require Enterprise, where prepaid credits at $1 each replace the usual seat math.
Snyk In-Depth Review 2026
Snyk is a security platform that scans code, open source dependencies, containers, and infrastructure-as-code from the IDE, the command line, source code managers, and CI/CD pipelines. Its DeepCode AI engine powers static analysis and automated fixes, while a large vulnerability database backs the dependency checks. A listing of 109 integrations covers GitHub, GitLab, Jenkins, Jira, and Kubernetes, so it slots into tools teams already run. Newer Evo features extend coverage to AI coding agents and AI-generated code.
What It's Like Day-to-Day
The core appeal, cited in more than 400 reviews, is that findings show up where developers already work. A vulnerable package gets flagged in the editor while you're still writing the import, and the result arrives with a suggested fix instead of a bare CVE number. That matters because busy engineers tend to ignore alerts that don't say what to do, and G2 reviewers praise the immediacy, with one saying the IDE *"tells me exactly what's wrong and how to fix it immediately.
Snyk Security & Compliance
Verified Compliance
- ISO 27001
- ISO 27017
- SOC 2 Type II
Security Features
- Regional hosting and data residency (US, EU, AU)
- Public Trust Center and subprocessor list
Privacy Commitments
- AI models trained on permissively licensed open source projects, never customer data
- GDPR compliant
Snyk: Frequently Asked Questions (FAQs)
Does Snyk have a free plan?
Yes, Snyk offers a Free plan at $0/month with access to SCA, SAST, IaC and Container scanning, 5 projects and 100 Snyk Code tests per month. No credit card is required to sign up.
How much does the Snyk Team plan cost?
The Snyk Team plan starts at $25/month billed monthly. It is for teams of up to 10 developers and includes 100 projects, 1,000 Snyk Code tests per month, Jira integration and next business day support.
How does Snyk Enterprise pricing work?
Snyk Enterprise uses prepaid credits where 1 credit = $1, usable across any Snyk capability. Pricing requires contacting sales, and rates are per Active Contributor per Day for Code, Open Source, IaC, Secrets and AI-SPM, among others.
What happens when my Snyk credits run out?
Running out of prepaid credits does not cut off access. Extra usage is tracked as on-demand consumption and invoiced in arrears, and you can top up mid-contract through your Snyk account team.
Snyk Integrations
| GitHub | GitLab | Bitbucket |
| Azure Repos | Jira | Slack |
| Jenkins | CircleCI | GitHub Actions |
| Azure Pipelines | AWS CodePipeline | Docker Hub |
| Amazon ECR | Kubernetes | Terraform Cloud |
| IntelliJ | Eclipse | Cursor |
| Claude | Google Gemini Code Assist | Amazon Q Developer |
| ServiceNow | Snowflake |
Snyk: Verified Data Sheet
| # | Label | Data Point |
|---|---|---|
| [1] | Snyk Consensus: 8.78/10 | Snyk is a highly-rated tool among AI coding tools in the Tooliverse index, with a consensus score of 8.78/10 across 1,795 verified reviews. |
| [2] | What is Snyk | Snyk, operated by Snyk Limited, is a SOC 2 Type II AI security platform that secures AI-generated code, agents and applications. It offers a free plan, with Team from $25/month and credit-based Enterprise pricing. |
| [3] | Tooliverse Consensus on Snyk | Snyk puts security findings where developers already work, pairing IDE and CI/CD scanning with fix suggestions and automated pull requests that shrink the gap between detection and repair. Reviewers single out its deep vulnerability database and container and infrastructure-as-code coverage as reasons it earns a spot in production pipelines. The catches are real: enterprise pricing strains smaller budgets, false positives demand manual triage, and large repositories can slow the IDE. Teams that budget for tuning get a scanner developers actually act on. |
| [4] | Snyk Verdict | Snyk bottom line: A top-tier developer-first security scanner whose actionable fixes and CI/CD integration win over engineers, though steep enterprise pricing and occasional false positives mean smaller teams should start with the cheaper plans. |
| [5] | Free: Free | Snyk offers a functional Free tier covering Access to SCA, SAST, IaC & Container scanning and Real-time code scanning, putting AI tools within reach at no cost. |
| [6] | Container and IaC scanning coverage | Snyk scans containers and infrastructure-as-code files alongside code and dependencies, giving full-stack security coverage according to 294 user reviews. |
| [7] | Large, frequently updated vulnerability database | Snyk draws on a large, frequently updated vulnerability database that 215 user reviews credit for reliable threat detection. |
| [8] | Automated CI/CD security checks | Snyk automates security checks inside CI/CD pipelines, helping teams maintain high deployment velocity, according to 198 user reviews, and it lists 109 integrations including GitHub, GitLab, Jenkins and CircleCI. |
| [9] | Team: $25/month | Snyk Limited's Team plan adds Increased test limits per product for just $25 monthly, significantly expanding on the free tier's capabilities. |
| [10] | Catches vulnerabilities inside developer workflows | Snyk integrates directly into developer workflows through its IDE, CLI and source code manager connections, catching vulnerabilities before they reach production, a strength validated by 412 user reviews. |
| [11] | Enterprise pricing strains smaller budgets | Snyk Enterprise pricing is credit-based (1 credit = $1) and requires contacting sales, and 156 user reviews describe the Enterprise tiers as prohibitively expensive for smaller organizations; the Team plan at $25/month is capped at 10 developers. |
| [12] | False positives need manual triage | Snyk generates occasional false positives that require manual triage and investigation, according to 112 user reports. |
| [13] | ISO 27001 | Snyk maintains ISO 27001, ISO 27017, and SOC 2 Type II certifications. |
| [14] | Enterprise: Regional hosting and data residency (US, EU, AU) | Snyk delivers enterprise security with Regional hosting and data residency (US, EU, AU) along with a Public Trust Center and subprocessor list. |
| [15] | IDE shows exactly what to fix | Snyk "completely changed how we handle security," with the IDE telling developers "exactly what's wrong and how to fix it immediately," according to a verified G2 reviewer. |
Best Snyk Alternatives
Aikido Security
Secure everything devs build, ship, and run—without drowning in false positives.
SonarQube
Catch bugs and vulnerabilities in AI-generated and human code before they ever reach production.
Sourcery
Perfectionist AI code review that catches bugs and security issues before they ever merge.