SonarQube Review 2026 - AI Code Verification
Verified Oct 20, 2026 by Tooliverse Editorial
SonarQube is the verification layer for the AI coding era, reviewing every pull request for bugs, vulnerabilities, and secrets. Trusted by 7M+ developers, it works in your IDE, CI/CD pipeline, and even with AI coding agents.
Activate and configure the SonarQube Remediation Agent | step-by-step setup guide
SonarQube Cloud Setup with GitHub Actions: Complete DevOps Tutorial 2026
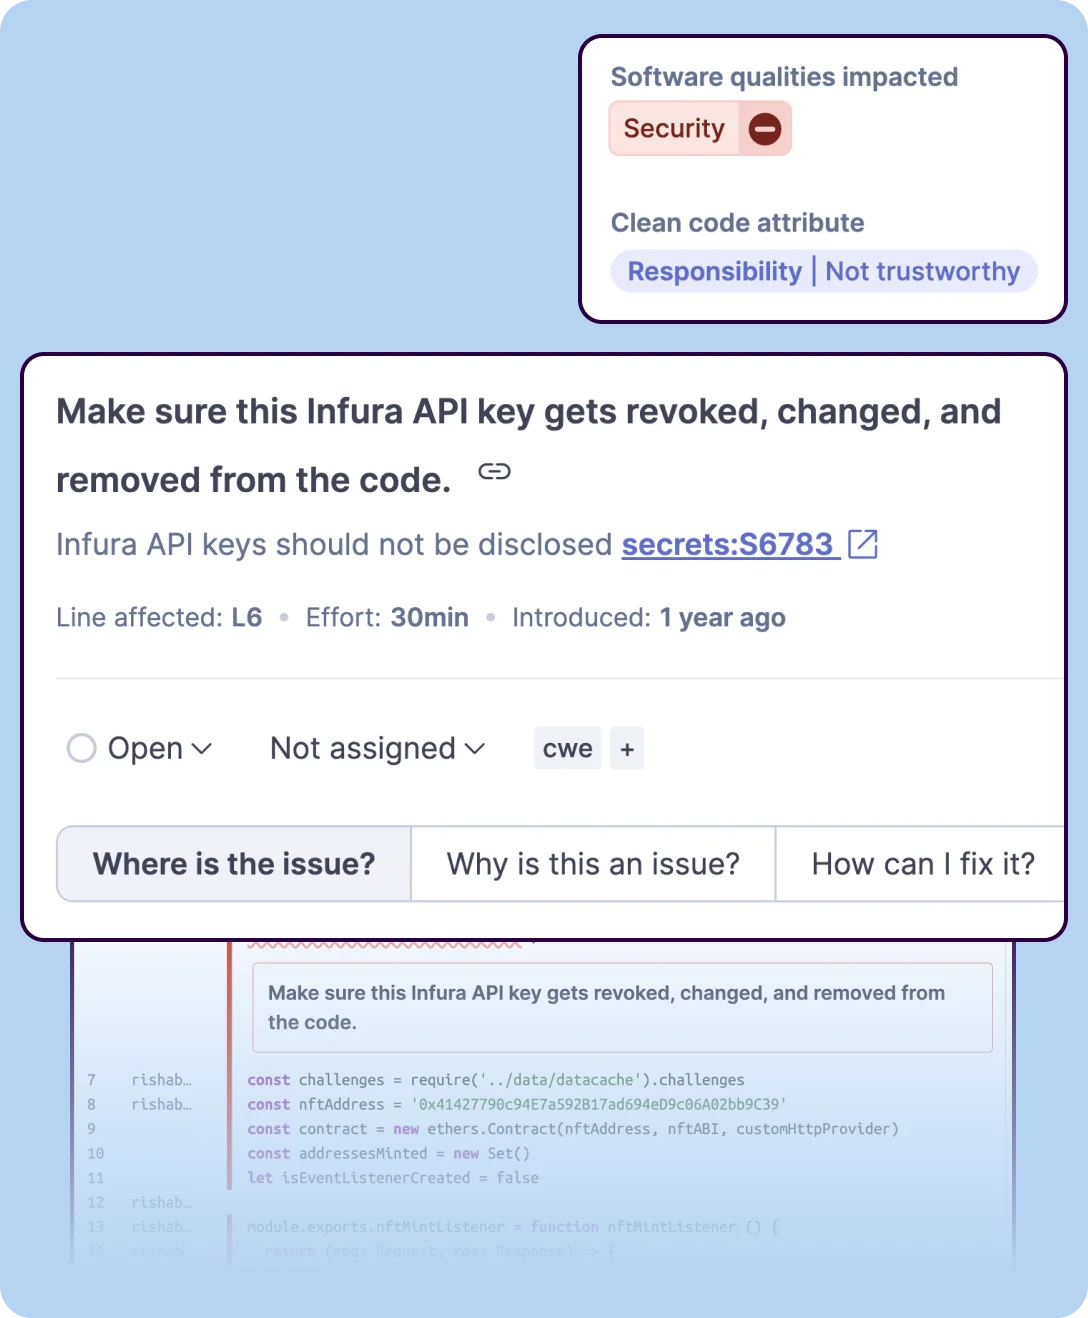
Identify and manage critical security vulnerabilities like exposed API keys.
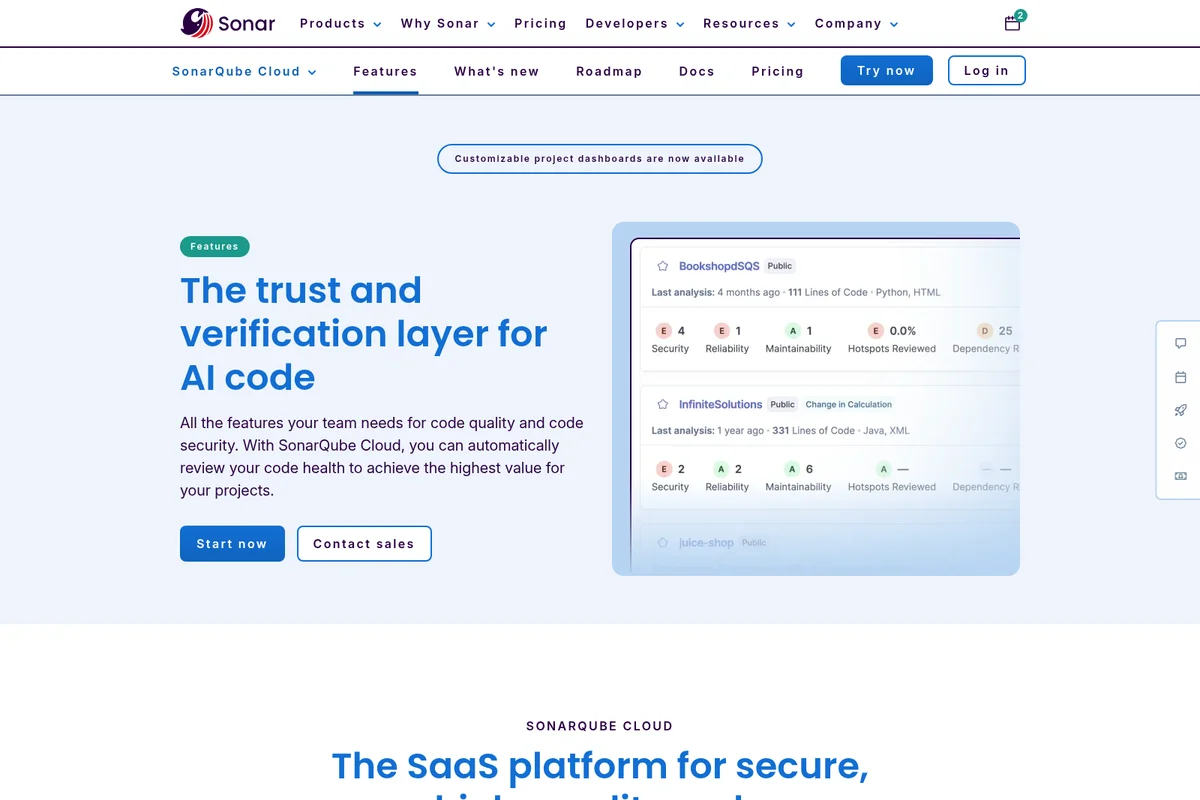
Gain a clear overview of your AI code's health with detailed quality metrics.
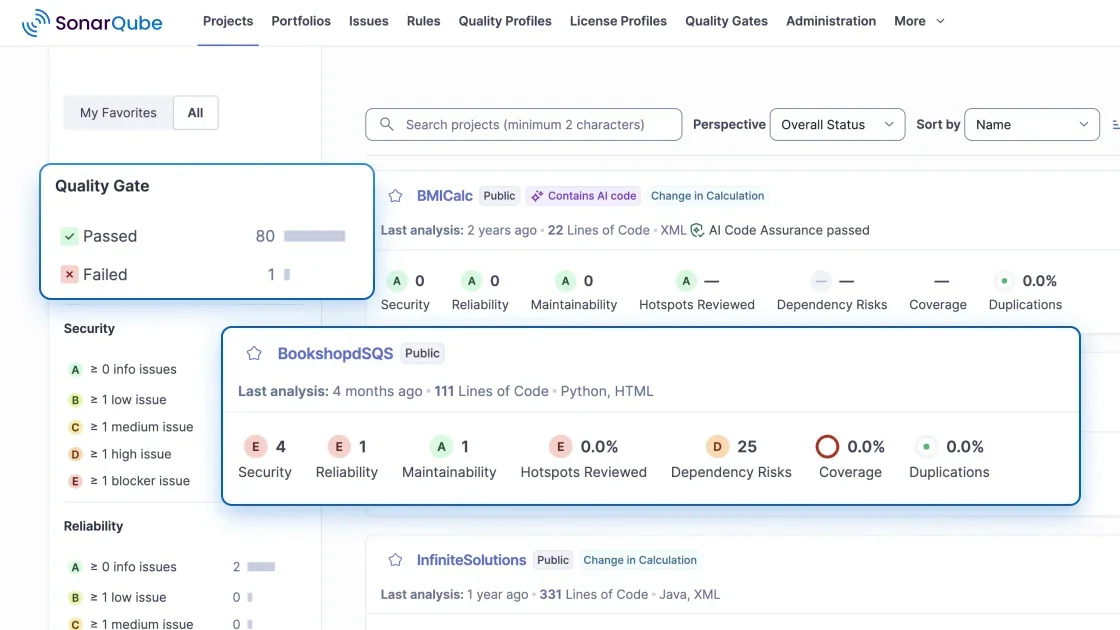
Monitor code quality across all your projects with real-time metrics.
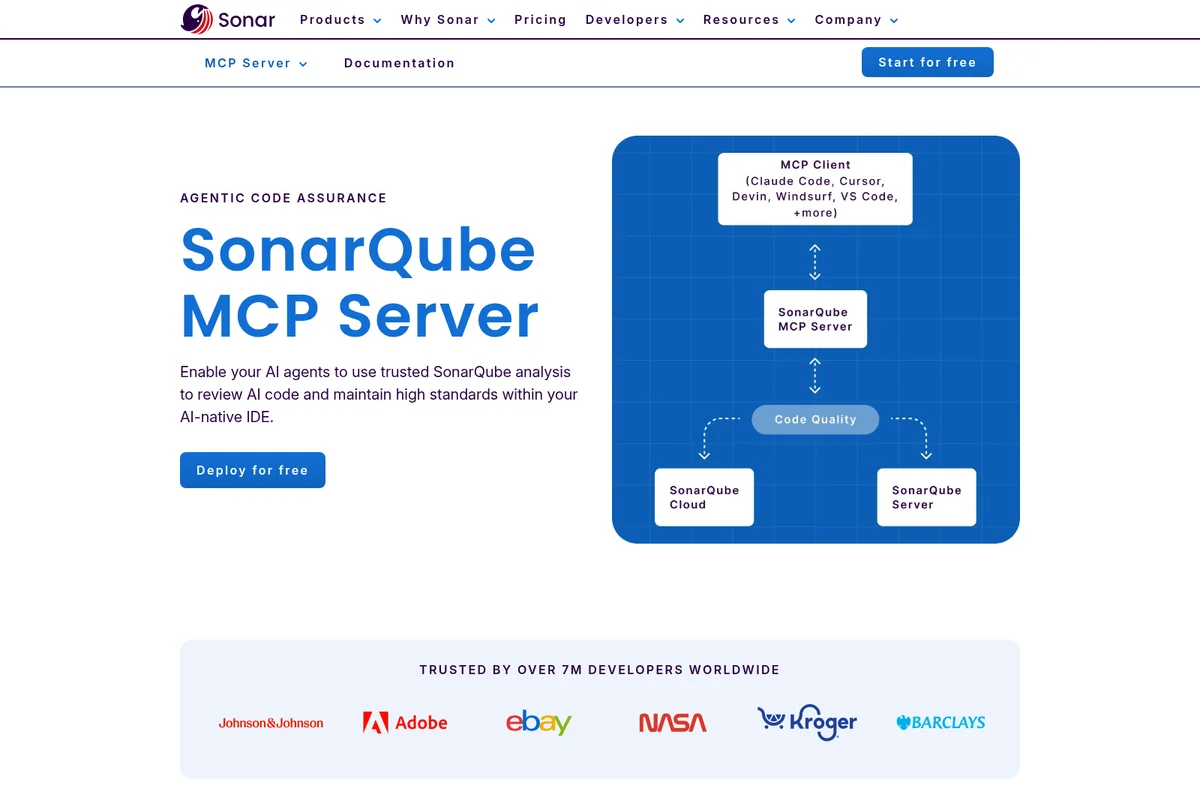
Enable AI agents to leverage SonarQube analysis for high-standard code reviews.
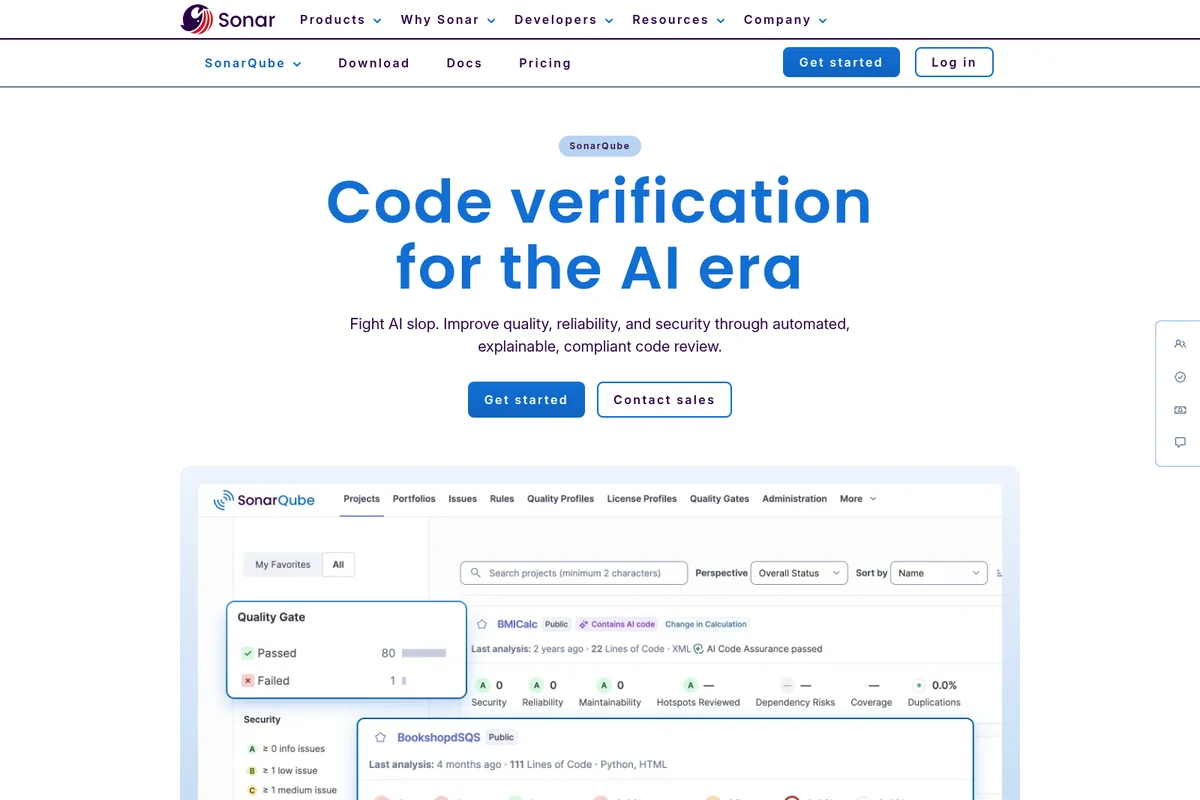
Monitor code quality, reliability, and security across all your projects.
SonarQube Review: Tooliverse Consensus




Based on 880 verified reviews across 5 platforms,
combined with Tooliverse's expert analysis
SonarQube works as the quality checkpoint between a developer's commit and production, turning coding standards into pass-or-fail gates that teams actually follow. Reviewers credit its security analysis, CI/CD integration and technical debt visualizations, and the Clean as You Code approach keeps legacy mess from blocking new work. The costs are real: it can strain build agents on large codebases, initial database setup has a learning curve, and some security rules need manual suppression.
Bottom line: One of the strongest code quality gatekeepers for CI/CD-driven teams, with deep security analysis and strict Quality Gates, though large codebases demand hefty build agents and a patient initial setup.
SonarQube | Key Specs
- Platforms
- Web, API (Cloud SaaS or self-hosted Server)
- Pricing Model
- Freemium ($0-34+/mo, Enterprise custom) See plans
- Privacy/Data Use
- Zero data retention and BYOK (Enterprise), full data residency on Server
- Security
- SOC 2 Type II, SAML SSO, air-gapped deployment See details
Wins
- •Provides deep static analysis that identifies critical security vulnerabilities before they reach productionmentioned in 310 reviews
- •Integrates seamlessly with major CI/CD pipelines to automate quality checks within developer workflowsmentioned in 245 reviews
- •Enforces the 'Clean as You Code' methodology through customizable and strict Quality Gatesmentioned in 190 reviews
Watch-Outs
- •Demands significant system resources which can slow down build agents on large codebasesmentioned in 95 reviews
- •Requires a steep learning curve for complex initial configuration and database setupmentioned in 80 reviews
- •Generates occasional false positives in security rules that require manual review and suppressionmentioned in 72 reviews
SonarQube Features 2026
Automated Code Review
Automatically scans all branches and pull requests, applies curated rules, and provides feedback in existing DevOps tools.
Quality Gates
Customizable go/no-go checks that fail pipelines when code does not meet quality and security standards.
Static Application Security Testing (SAST)
Finds OWASP Top 10 vulnerabilities such as injection, authentication flaws and XSS with taint analysis across files and functions.
Advanced SAST and SCA
Traces data flows into third-party libraries and detects CVEs, license risks and generates SBOMs.
SonarQube User Reviews
Selected Reviews
"The integration with our GitLab CI was flawless. It caught a critical SQL injection vulnerability in a PR that our manual review missed."
"It changed how our junior devs write code. They see the issues immediately in the IDE via SonarLint and fix them before even committing."
"The rule set is powerful but the false positive rate on some of the newer C# rules is frustrating. We spend too much time marking 'Won't Fix'."
More from the Community
"SonarQube is the backbone of our 'Clean as You Code' strategy. The Quality Gates are non-negotiable for us now."
"Great tool for tracking technical debt, but the Java heap requirements for scanning our monolith are insane. We had to upgrade our build agents twice."
"Supports almost every language we use, from COBOL to TypeScript. Essential for a multi-stack enterprise."
"Pricing for the Developer Edition jumped significantly this year. It's getting harder to justify for smaller teams when SonarCloud exists."
"The UI is a bit dated compared to modern SaaS tools, but the data depth is unmatched. I love the heatmaps for code coverage."
"Solid security analysis. It's our primary SAST tool. Setup was a bit of a headache with the database configuration though."
"The best way to visualize technical debt over time. The trend charts help me explain to management why we need a refactoring sprint."
"Reliable and robust. We've been using it for years and the 2026 updates to the AI-driven code suggestions are actually quite helpful."
"Essential for compliance. We use the PDF reports for our audits and it saves us weeks of manual documentation."
SonarQube Pricing 2026
The free tier covers private projects up to 50k lines of code with no credit card, enough to find out whether Quality Gates fit how your team ships. Team at $34/month raises the ceiling to 100k lines and suits groups under 50 developers who want pull request analysis without a sales call. Enterprise adds SSO, SCIM, portfolios and commercial support, so it matters mainly once procurement or compliance gets involved.
SonarQube In-Depth Review 2026
SonarQube, built by SonarSource, scans code for bugs, vulnerabilities, code smells and exposed secrets, then blocks merges that miss the standard. It covers more than 40 languages, frameworks and infrastructure-as-code platforms, and applies the same rules in the IDE, on pull requests and in CI/CD pipelines on GitHub, GitLab, Bitbucket and Azure DevOps. It runs as a managed cloud service or as self-hosted Server editions, and it holds AI-generated code to the same checks as human-written code.
What It's Like Day-to-Day
Most of the time, SonarQube stays out of sight until something fails. A developer pushes a branch, analysis runs in the pipeline, and the results land on the pull request next to the diff. Security findings are the capability reviewers mention most, in 310 reviews, and one G2 reviewer said the tool "caught a critical SQL injection vulnerability in a PR that our manual review missed". That is the pitch in one sentence: a second pair of eyes that never skims.
Quality Gates are the mechanism that makes the habit stick.
SonarQube Security & Compliance
Verified Compliance
- SOC 2 Type II (SonarQube Cloud)
Security Features
- SAML SSO (Enterprise)
- Air-gapped deployment options (Server)
- 99.9% uptime SLA (Cloud)
Privacy Commitments
- Zero data retention and BYOK with LLMs (Enterprise)
- Complete data residency and privacy control with SonarQube Server
SonarQube: Frequently Asked Questions (FAQs)
Is SonarQube free?
Yes, SonarQube offers several free options. SonarQube for IDE is always free, SonarQube Cloud has a free tier for private projects up to 50k LOC, and the Community Build is a free open source edition. Free trials are also available for Cloud and Server.
How much does SonarQube cost?
SonarQube Cloud Team plan pricing starts at $34 monthly for up to 100k LOC, with a 14-day trial. Enterprise is custom-priced through sales. Server editions are priced per instance per year based on lines of code.
Does SonarQube offer a self-hosted option and how is it priced?
Yes, SonarQube Server is the self-managed option, available in Developer, Enterprise and Data Center editions priced per instance per year based on LOC. A free Community Build is also available.
How are lines of code counted for billing?
Only LOC from private projects count toward billing, and for projects with branches only the largest branch is counted. Analysis frequency does not affect the count.
SonarQube Integrations
| GitHub | GitLab | Bitbucket |
| Azure DevOps | VS Code | Visual Studio |
| IntelliJ IDEA | Eclipse | Cursor |
| Windsurf | Claude Code | GitHub Copilot |
| Gemini CLI | GitHub Actions | Docker |
| Kubernetes |
SonarQube: Verified Data Sheet
| # | Label | Data Point |
|---|---|---|
| [1] | SonarQube Consensus: 8.80/10 | SonarQube is a highly-rated tool among AI coding tools in the Tooliverse index, with a consensus score of 8.80/10 across 880 verified reviews. |
| [2] | What is SonarQube | SonarQube, by SonarSource, is a SOC 2 Type II code quality and security platform with SAST, secrets detection and AI code review. It is trusted by 7M+ developers, with a free tier and Team plan from $34/month. |
| [3] | Tooliverse Consensus on SonarQube | SonarQube works as the quality checkpoint between a developer's commit and production, turning coding standards into pass-or-fail gates that teams actually follow. Reviewers credit its security analysis, CI/CD integration and technical debt visualizations, and the Clean as You Code approach keeps legacy mess from blocking new work. The costs are real: it can strain build agents on large codebases, initial database setup has a learning curve, and some security rules need manual suppression. |
| [4] | SonarQube Verdict | SonarQube bottom line: One of the strongest code quality gatekeepers for CI/CD-driven teams, with deep security analysis and strict Quality Gates, though large codebases demand hefty build agents and a patient initial setup. |
| [5] | Free (Developers): Free | SonarQube offers a Free (Developers) tier that brings SonarQube Team plan features to private projects, with up to 50k lines of code, at no cost. |
| [6] | Strict Quality Gates enforce Clean as You Code | SonarQube enforces the Clean as You Code methodology through customizable go/no-go Quality Gates that fail pipelines when new code misses quality and security standards, a capability praised in 190 user reviews. |
| [7] | 40+ languages for unified reporting | SonarQube supports 40+ languages, frameworks and IaC platforms for consistent enterprise-wide reporting, with 30+ languages covered on every pull request in the Team plan and 45+ on Enterprise Cloud, according to 155 user reviews. |
| [8] | Technical debt and coverage visualizations | SonarQube visualizes technical debt and code coverage through trend charts and heatmaps that guide refactoring decisions, a benefit highlighted in 120 user reviews. |
| [9] | Team (Cloud): $34/month | SonarSource's SonarQube Team (Cloud) is built for teams under 50 developers, requires no sales call, and costs $34 monthly, expanding significantly on the free tier's capabilities. |
| [10] | Deep SAST catches vulnerabilities pre-production | SonarQube performs deep static analysis, including taint analysis for OWASP Top 10 flaws such as injection, authentication flaws and XSS, and catches critical security vulnerabilities before they reach production, a strength cited in 310 user reviews. |
| [11] | High resource demands on large codebases | SonarQube can demand significant system resources, and user reports indicate analysis may slow build agents on large codebases, according to 95 user reviews. |
| [12] | Steep initial configuration and database setup | SonarQube presents a steep learning curve for complex initial configuration and database setup, according to 80 user reviews; the self-managed SonarQube Server carries most of this burden. |
| [13] | SOC 2 Type II (SonarQube Cloud) | SonarQube holds SOC 2 Type II (SonarQube Cloud) certification. |
| [14] | Enterprise: SAML SSO (Enterprise) | SonarQube provides enterprise security with SAML SSO (Enterprise), Air-gapped deployment options (Server), and a 99.9% uptime SLA (Cloud). |
| [15] | Caught a SQL injection manual review missed | A verified G2 reviewer noted that SonarQube's GitLab CI integration "was flawless" and "caught a critical SQL injection vulnerability in a PR that our manual review missed." |
Best SonarQube Alternatives
Snyk
Ship AI-generated code with confidence, knowing every line, agent, and app is secured.
Aikido Security
Secure everything devs build, ship, and run—without drowning in false positives.
CodeScene
Keep AI-generated code healthy and ship faster with the only code metric proven to predict defects and delivery performance.